The cybersecurity platform that protects your DNS traffic inside your organization

Obsolix monitors DNS queries in real time and detects, blocks and reports malicious domains with threat intelligence, behavioral analysis and AI. All analysis runs on your own servers; not a single record leaves your organization.

Obsolix logoObsolix

On-Premises DNS Security Platform

Developed in Türkiye by Ankara-based Korsis Teknoloji. Manage detection, blocking and reporting at the DNS layer from a single point, entirely inside your organization.

Obsolix DNS security platform visual

Obsolix is a DNS security platform that monitors and analyzes your organization's DNS traffic in real time. It detects malicious domains using national and international threat intelligence, behavioral analysis and on-premises AI, then blocks, quarantines and reports them.

All analysis is done on your own servers; DNS logs, user mappings and analysis results never leave your organization. It scales to branches with the Edge + Central architecture, runs even on air-gapped networks and integrates with your existing SIEM and Active Directory.

OBSOLIX

DNS Security That Keeps Your Data In-House

Makes the DNS layer visible and stops threats inside your organization.

  • Real-time DNS monitoring and blocking
  • DGA, DNS tunneling and NXDOMAIN storm detection
  • Fast-flux and brand impersonation domain detection
  • Explainable decisions with on-premises AI
  • SIEM, Active Directory and scheduled reports
  • 100%

    of analysis in-house

  • Edge + Central

    runs on multi-branch networks

  • 200,000+

    users at a live deployment

  • TR / EN / AR

    Turkish, English, Arabic interface

WHY OBSOLIX?

Why Obsolix?

Recognizes known threats instantly and unknown ones by their behavior, and makes every decision inside your organization.

  • Threat Intelligence

    Known threats are blocked instantly with malicious domain lists continuously updated from national and international threat intelligence sources.

  • On-Premises AI

    A machine learning model that scores DNS traffic behavior runs on your own server, and the reasoning behind every decision is visible. It does not connect to any external AI service.

  • Behavioral Analysis

    DGA domains, DNS tunneling, NXDOMAIN storms, fast-flux and brand impersonation domains are caught in real time and quarantined automatically.

  • On-Premises Deployment

    Runs on your own servers, even on air-gapped networks. Data never leaves the country; it complies with KVKK and Turkish public-sector information security regulations.

  • Architecture That Scales to Branches

    One Edge per site, one console at the center. When the link drops, logs wait locally and are delivered without loss once it is back.

  • Works With Your Existing Systems

    CEF / LEEF / Syslog to your SIEM; agentless user mapping with Active Directory; Excel and PDF reports; email digests.

INTERFACE

The Obsolix Interface

Every module is managed from a single interface.

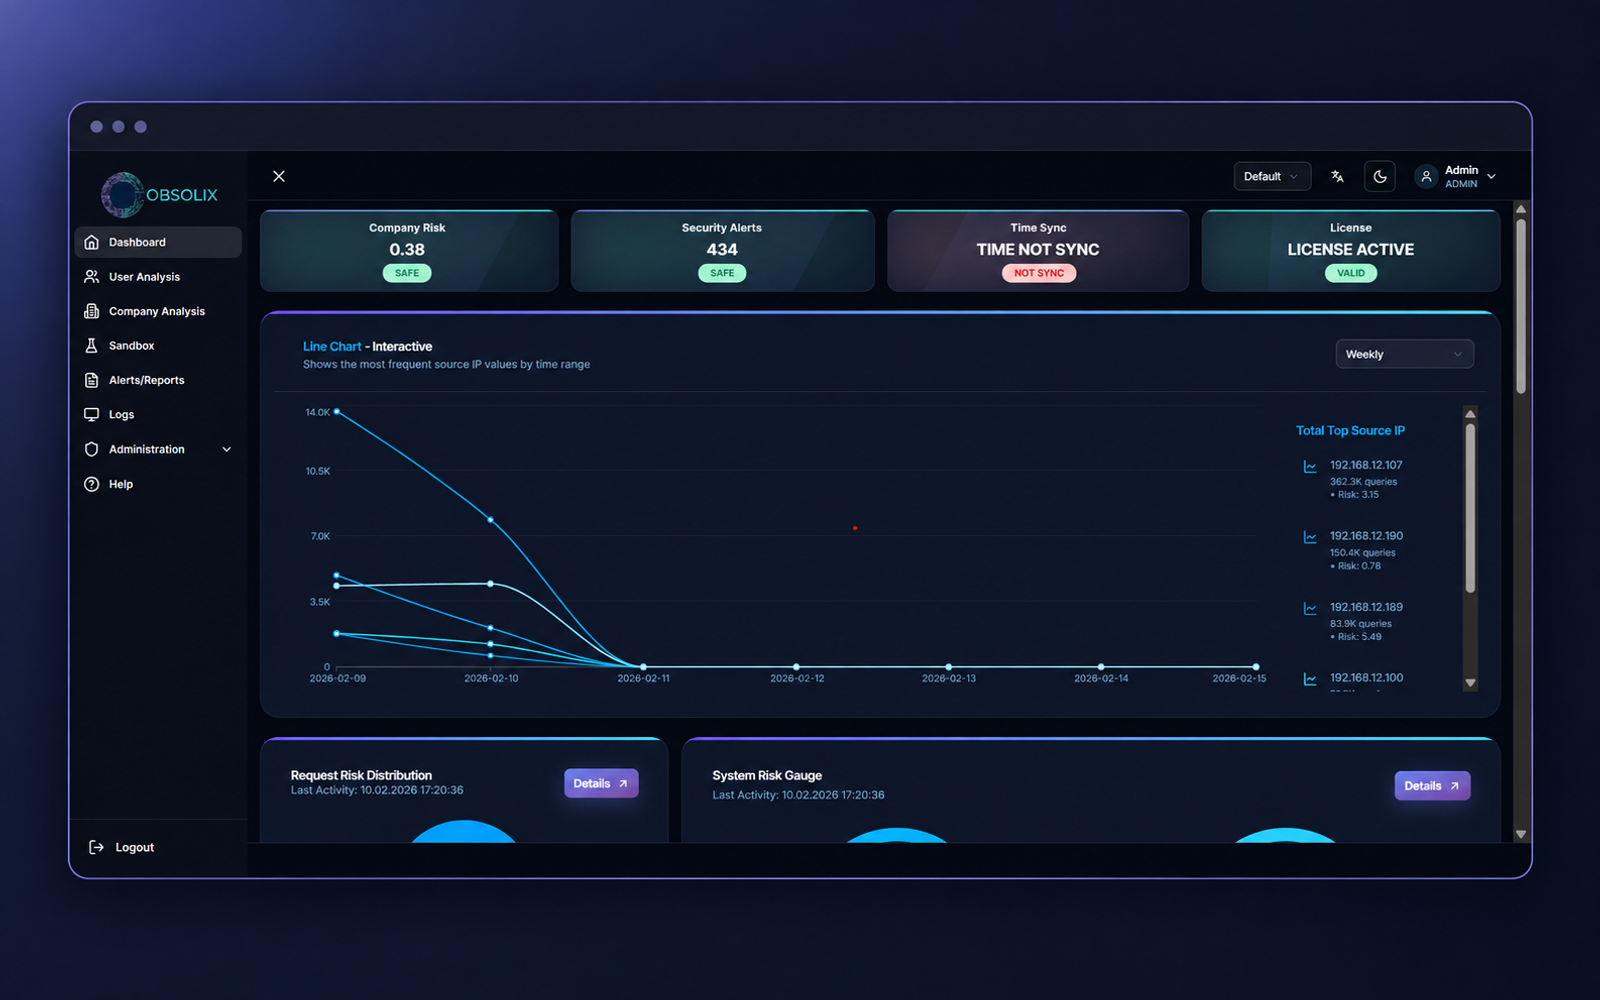
  • Obsolix Dashboard screen: live threat summary and edge health for every site

    Dashboard

    Live threat status, edge health and a daily summary for every site on one screen.

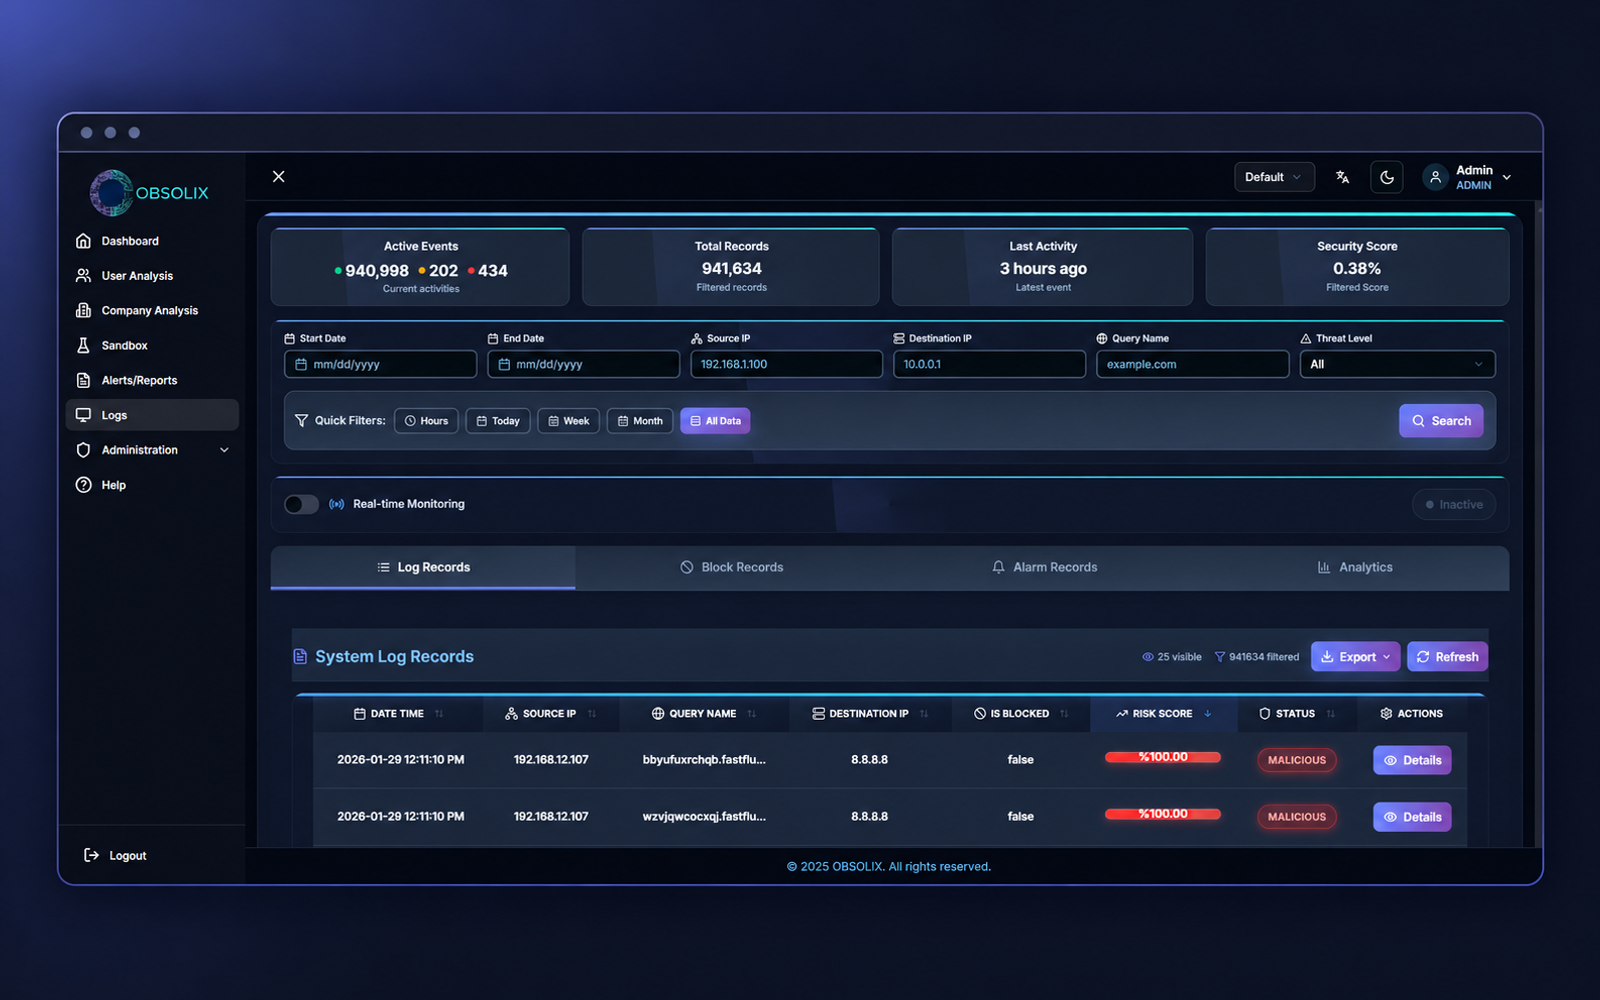
  • Obsolix Logs screen: DNS queries searchable by source, user, verdict and reason

    Logs

    Every DNS query is searchable by source, user, verdict and reason, and can be exported to Excel.

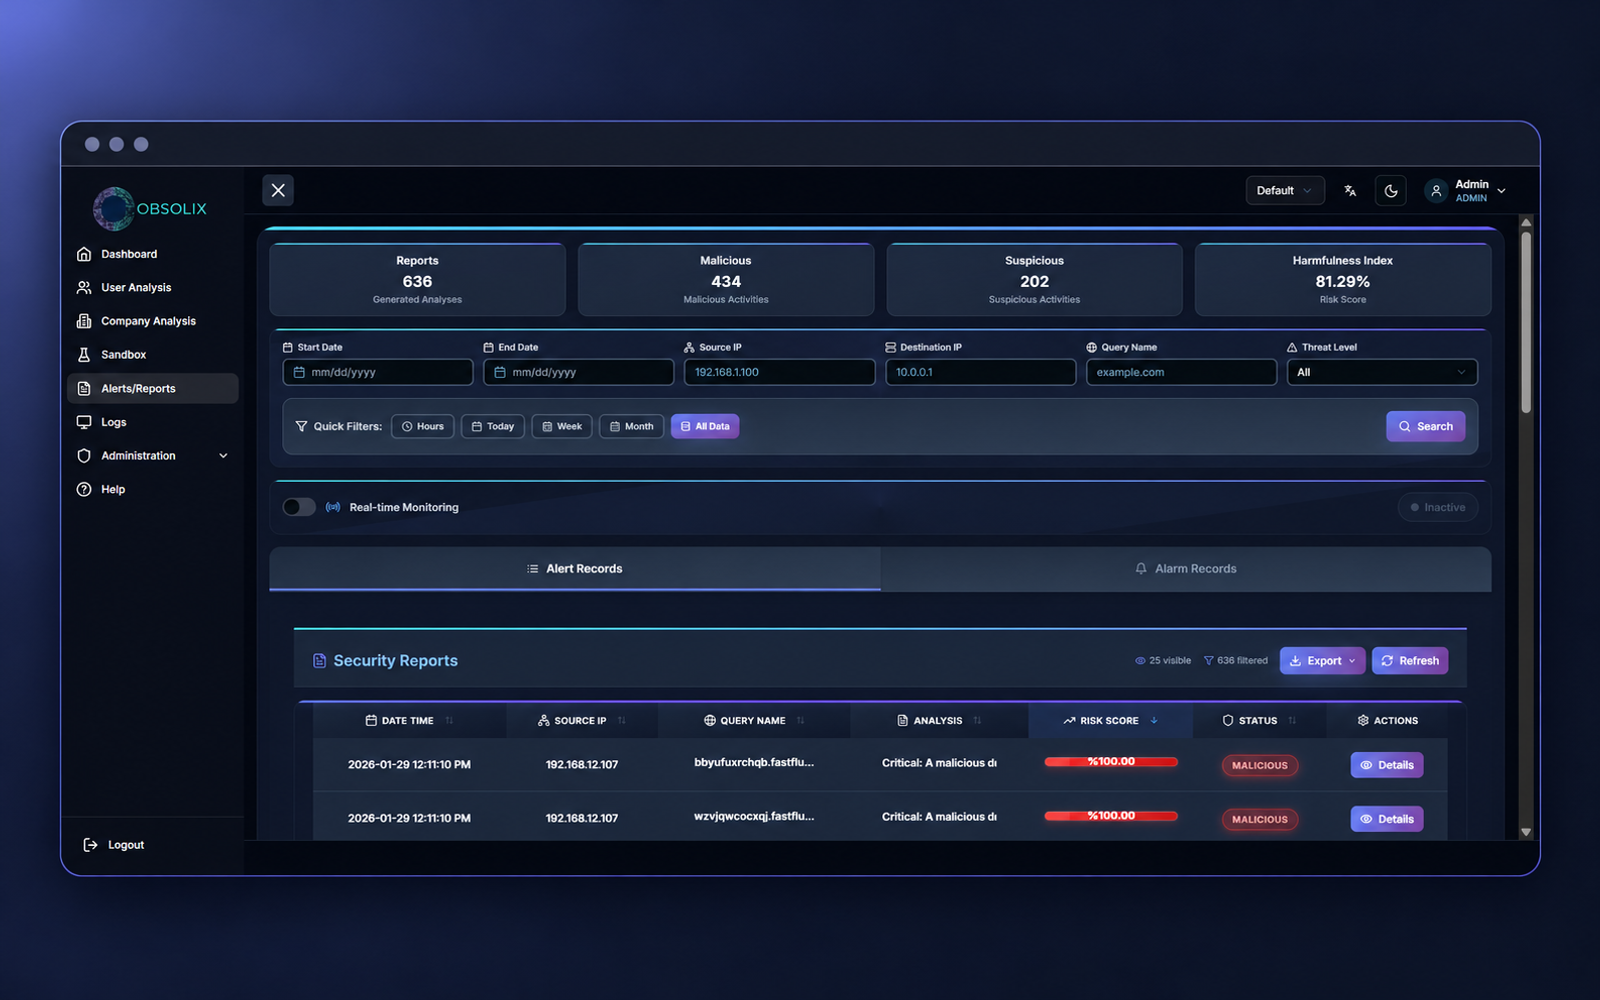
  • Obsolix Alerts screen: quarantine, blacklist and block events

    Alerts

    Quarantine, blacklist and block events in separate tabs, forwarded to your SIEM instantly.

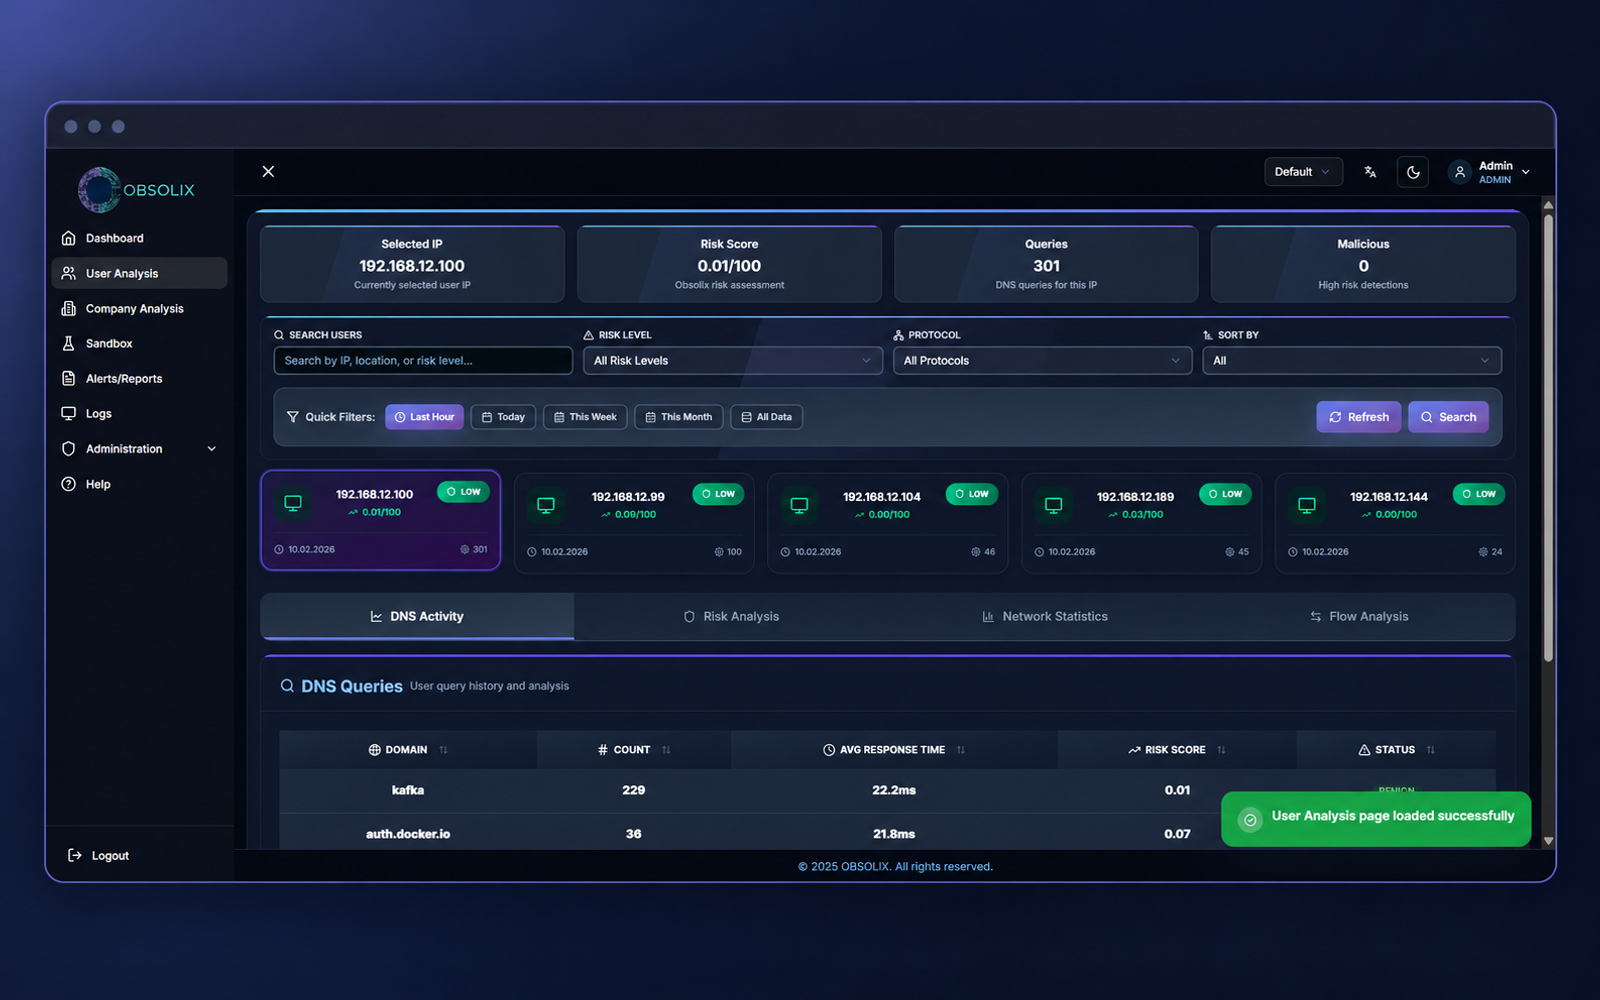
  • Obsolix User Analysis screen: per-user risk score and query profile

    User Analysis

    Per-user risk score, query profile and timeline; user names are shown via Active Directory mapping.

See all modules

WHO IS IT FOR?

Who Is It For?

Designed for every organization whose data must stay in-house.

  • Public Institutions

    Data must not leave the institution; Obsolix complies with public-sector information security regulations.

  • Finance

    Regulatory constraints and 24/7 visibility; with the branch architecture, every location is monitored centrally.

  • Defense and Critical Infrastructure

    Offline installation and updates on air-gapped networks.

  • Healthcare and Education

    The DNS traffic of thousands of users, managed with per-user risk scores and reports.

Obsolix is live at a public institution with more than 200,000 users, running on a multi-branch Edge + Central architecture.

References

FAQ

Frequently Asked Questions

Short answers; more on the FAQ page.

What is Obsolix?

A DNS security platform that runs inside your organization. It monitors DNS queries in real time and detects, blocks and reports malicious domains using threat intelligence and behavioral analysis. It is developed in Türkiye by Ankara-based Korsis Teknoloji.

Does my data leave the country?

No. Logs, user identities and analysis results stay only on your organization's servers. The system sends no data out; it only downloads threat intelligence updates.

We already have a firewall and a DNS security subscription. Why would we need Obsolix?

Global DNS security services such as Palo Alto, Cisco Umbrella and Cloudflare run their analysis in the vendor's cloud and send your logs there. Obsolix stops the same threats inside your organization, works on air-gapped networks and is independent of your firewall brand. It works alongside your existing systems.

All questions

Protect your DNS layer today

Talk to our team about a deployment scenario for your organization; Obsolix goes live without changing your existing infrastructure.